OpenRouter API Key: Get It, Limit It, Keep It Secret
An OpenRouter API key is a secret that lets your app call AI models through OpenRouter and spend your credits. Give every key a credit limit and keep it on your server, never in frontend code.

On this page
- What is an OpenRouter API key?
- How to get (create) an OpenRouter API key
- Is an OpenRouter API key free?
- Why every OpenRouter key needs a credit limit
- Can you put an OpenRouter key in frontend code? We tested it.
- What the Railway incident means for your OpenRouter key
- Leaked an OpenRouter key? Do this now
- FAQ
- Check your app before launch
An OpenRouter API key is the secret your app sends to OpenRouter to call AI models, and every request it makes can spend your credits. So the rules are simple: create one key per app, give it a credit limit, and keep it on a server. We built three small demo apps with a fake OpenRouter key and scanned them to show where a key leaks and where it doesn't.
By Gary, Greenlight My App · Updated Oct 28, 2026 · How we checked this: on Oct 28, 2026 (about 7:02 to 7:10 AM ET) we built three local demo apps with an obviously fake key, made of X characters, and ran the Greenlight My App scanner on each. No OpenRouter account, no real key and no request to OpenRouter's API. OpenRouter's docs and Railway's incident pages were read the same morning without signing in. Drafted with AI tools and reviewed by a person before publishing.
What is an OpenRouter API key?
An OpenRouter API key is a secret token that identifies your account when your app calls OpenRouter's API. OpenRouter's docs say requests authenticate with it as a Bearer token, and that its keys can carry credit limits. Whoever has the key can make requests that spend your credits.
OpenRouter gives one API in front of many AI models, so a single key can reach models from several providers. OpenRouter's docs put it this way: API keys on OpenRouter are "more powerful than keys used directly for model APIs", because they let you set credit limits for apps and can be used in OAuth flows.
That makes it a secret key, not a public one. If you want the general difference between public and secret keys, see what an API key is (external). The same rules apply to an OpenAI API key (external) or a Claude API key (external).
How to get (create) an OpenRouter API key
Sign in to OpenRouter, open your key settings page and create a new key. OpenRouter's docs say to give it a name and choose a credit limit, or no limit. Then store the key in a server environment variable, not in your code. Keys created for you during onboarding get a $100 credit limit and expire after 180 days.
- Sign in to your OpenRouter account and go to your API key settings page.
- Create a key and give it a name that says which app uses it, such as
my-app-production. - Choose a credit limit. OpenRouter's docs say you can also use a daily, weekly or monthly limit that resets.
- Copy the key into your server's environment variables or your host's secrets settings, for example
OPENROUTER_API_KEY. - Send it from your server as
Authorization: Bearer <your key>.

We didn't sign in or create a real key for this guide, so we don't show the dashboard. Follow the menu names you see on OpenRouter's site.
Is an OpenRouter API key free?
OpenRouter's docs we checked don't list a charge for creating a key. Using it is another matter: requests spend credits from your account balance. Free model variants, with IDs ending in :free, have request limits instead: 20 per minute, and 50 or 1,000 per day depending on credits bought.
So an "OpenRouter free API key" really means a key used only with free model variants. OpenRouter's limits page, checked Oct 28, 2026:
Free model variant (:free) | Limit |
|---|---|
| Requests per minute | 20 |
| Requests per day, if you've bought less than 10 credits in total | 50 |
| Requests per day, if you've bought at least 10 credits | 1,000 |
Prices and limits as of Oct 28, 2026. Check the official page before you rely on them.

Same page: errors tell you which limit you hit. A 402 means a credit limit, a 403 means a budget limit an admin set, and a 429 means a rate limit. A leaked key on free models alone can still use up your daily free requests, and a key with credits behind it can spend them.
Why every OpenRouter key needs a credit limit
OpenRouter's docs recommend a credit limit on every key, because a key with no limit lets a leaked key or a runaway agent spend your entire balance, including any auto top-ups. Once a key reaches its limit, OpenRouter rejects its requests until you raise the limit or a reset period passes.
A credit limit is your backstop if everything else fails. It doesn't stop a key from leaking, but it caps what a leak can cost. Practical setup:
- One key per app and per environment. If one leaks, you replace one key, not all of them.
- A limit sized to normal use. Pick a daily, weekly or monthly reset that covers a normal period with room to spare.
- No-limit keys stay on servers. OpenRouter's docs say that if you need a key without a limit, keep it out of client-side code and rotate it promptly if you think it was exposed.
Here is how a key flows in a safe setup, and the two ways it most often leaks:
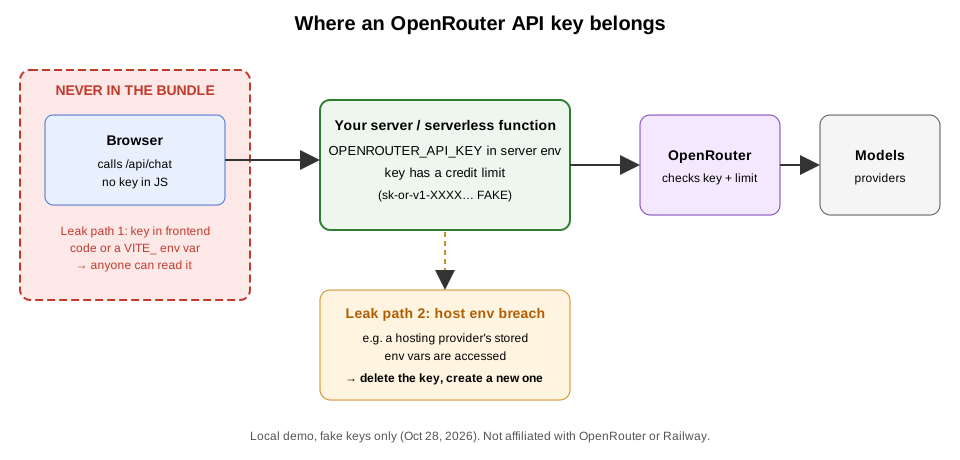 Keep the key on the server, with a limit. Original diagram by Greenlight My App (fake key shown as XXXX), Oct 28, 2026.
Can you put an OpenRouter key in frontend code? We tested it.
No. In our test, a fake OpenRouter key written into the page's JavaScript, and the same key in a VITE_ environment variable, both ended up in the code the browser downloads, and our scan flagged both. Only the version that called the model through our own server route kept the key out.
We built three versions of the same tiny chat page. Each used a fake key: our demo used a fake key starting with sk-or-v1-, followed by 64 X characters, labeled FAKE. None of them ever called OpenRouter.
| Version | Where the key lived | Key in the browser's code? | Greenlight My App scan |
|---|---|---|---|
| A. Inline | Hard-coded in app.js | Yes | FAIL: "OpenAI API key is visible in your public code" |
| B. Vite env variable | VITE_OPENROUTER_API_KEY in .env, then vite build | Yes, inside dist/assets/index-Cj3V1tWD.js | FAIL: "OpenAI API key is visible in your public code" |
| C. Server proxy | OPENROUTER_API_KEY in the server's environment; the page calls /api/chat | No | PASS: "No secret keys found in your public code" (2 files checked) |
Source: our local test, Oct 28, 2026 (Vite 7.3.7, Greenlight My App scanner, fake key only).
One honest note on the label: the scan flagged the key in A and B as an exposed secret, but it called it an "OpenAI API key", not an OpenRouter key. The finding was right that a secret key was public. The name was wrong. Our scan checked each homepage and up to 15 of the scripts it loads; we didn't test lazy-loaded files or source maps here.


Why B leaks: Vite's docs say VITE_ variables are bundled into your source code at build time and shouldn't hold API keys. Next.js's docs say NEXT_PUBLIC_ variables are inlined into the JavaScript sent to the browser at build time. Our .env file guide (external) explains both. Source maps can expose even more of your code, which our source maps guide (external) covers.
Want to check your own app? Run Greenlight My App's free scan on your live URL.
What the Railway incident means for your OpenRouter key
Railway reported that on Oct 21, 2026, an unauthorized party may have accessed encrypted environment variables and, for some, obtained the decrypted contents. Its preliminary report names OpenRouter among the providers it worked with to revoke potentially compromised keys. If your OpenRouter key was stored on Railway, follow Railway's advice and rotate it.
This is the second way keys leak: not from your frontend, but from where your server stores them. Here is what Railway's own pages say, as checked Oct 28, 2026:
- Railway's Oct 21 security disclosure (external) says it "strongly recommend[s]" that customers immediately roll all environment variables stored in Railway, including any API keys, plus any private registry credentials, and review their logs.
- Railway's preliminary report (external) says it worked with GitHub, GitLab, Anthropic, OpenAI, OpenRouter, SpaceXSI, Stripe and others to revoke the potentially compromised keys as soon as it knew they were accessed, on Oct 21 at 09:25 UTC (5:25 AM ET). It recommends that customers who signed up before Oct 21 rotate keys stored on Railway.


A credit limit wouldn't prevent a breach like this, but it limits what a stolen key could spend.
Leaked an OpenRouter key? Do this now
Delete the key in your OpenRouter key settings and create a new one, as OpenRouter's docs say. Put the new key only in server environment variables, give it a credit limit, then remove the old key from your code, Git history and every host where it was stored. Check your usage for requests you didn't make.
- Delete the exposed key and create a new one. OpenRouter's docs say to do this right away if you get a compromise notice or suspect exposure.
- Add a credit limit to the new key. Size it to normal use.
- Update every place the key lived: your host's environment settings, CI secrets, and any teammate's
.envfile. - Remove the old key from your code and frontend. Move OpenRouter calls behind a server route, like version C above.
- Check your usage and logs for requests you don't recognise.
- If you committed it to GitHub, still treat it as leaked. OpenRouter's docs say it is a GitHub secret scanning partner and emails you if it determines a key was compromised, but don't wait for that email.
- Check Activity by key. OpenRouter's Activity page lets you group usage by API key, so you can spot a key spending when it shouldn't.
- Delete keys you forgot about. OpenRouter lets you list your API keys and delete any of them; remove any key no app uses anymore.

The same steps work for other secret keys. See our guides to Claude API key security (external) and Stripe API keys (external). If you built with an AI tool, the Lovable launch checklist (external) covers keys and the rest of a pre-launch pass.
FAQ
Is it free to get an OpenRouter API key?
The OpenRouter docs pages we checked on Oct 28, 2026, don't list a charge for creating a key. Requests to paid models spend credits from your balance. Free model variants, with IDs ending in :free, are capped at 20 requests per minute and 50 or 1,000 per day, depending on how many credits you've bought.
Where do I find my OpenRouter API key?
Your keys live on your OpenRouter key settings page, where OpenRouter's docs say you create, limit and delete them. In your app, the key should sit in a server environment variable such as OPENROUTER_API_KEY, not in your code. If you can't find where your app stores it, search your project and your host's environment settings.
What does sk-or-v1 mean?
OpenRouter's API keys and limits pages, as we checked them on Oct 28, 2026, don't document a key format or prefix, so we can't say what each part means. Our demo used a fake key starting with sk-or-v1-. Treat any OpenRouter key as a secret, whatever it starts with.
Are an API key and a token the same? Not always, but here they work together. OpenRouter's docs say its API authenticates requests using Bearer tokens, and you send your API key as that token in the Authorization header. So for OpenRouter, the key is the token. Other services issue short-lived tokens separately from long-lived keys.
Can I put my OpenRouter key in frontend code?
No. In our test, a key written into the JavaScript and a key in a VITE_ variable both ended up in the code the browser downloads, where anyone can read it. Call OpenRouter from your own server route instead, and keep the key in that server's environment with a credit limit.
What should I do if my OpenRouter key leaks? Delete the key on your OpenRouter key settings page and create a new one, as OpenRouter's docs recommend. Give the new key a credit limit and store it only on your server. Then remove the old key from your code, Git history and hosts, and check your usage for requests you didn't make.
Check your app before launch
Calling OpenRouter from an app built with Lovable, Bolt, Cursor, Replit or v0? Scan your app before launch with Greenlight My App's free scan. It looks for secret keys that shouldn't be there in your homepage and up to 15 of the scripts it loads. The scan is automated, read-only and educational, not a security audit, and "nothing found" isn't a guarantee that nothing is exposed.
Sources
- OpenRouter docs: API keys and authentication (external)
- OpenRouter docs: API limits (external)
- Railway: Security disclosure, Wednesday October 21st (external)
- Railway: Preliminary report, October security incident (external)
- Vite docs: Env variables and modes (external)
- Next.js docs: Environment variables (external)
On this site
Related posts
Stripe API Keys: Test vs Live, Secret vs Publishable (2026)
Stripe API keys explained: test vs live, secret vs publishable, restricted keys and the webhook secret, plus what to do if a secret key leaks.
What Is an API Key? Public vs Secret Keys, Explained
What is an API key? A plain-English guide to public vs secret keys, what happens if one leaks, and how to check your app's code before launch.
How to Get an OpenAI API Key (and Keep It Safe)
How to get an OpenAI API key in 4 steps, then keep it out of your frontend, set a spend limit, and revoke it fast if it leaks.


Get the next change before it bites
Greenlight tips and new blog posts: short, practical notes when Supabase, Lovable, Bolt, Cursor or another tool you build with changes something that affects your app, plus what to check. About twice a month.
We'll send a confirmation email first. Unsubscribe anytime. Privacy. Greenlight My App is independent and not affiliated with or endorsed by Supabase, Lovable, Bolt, Cursor or any other tool we mention.
Greenlight My App is independent and not affiliated with or endorsed by OpenRouter, Railway, OpenAI, GitHub, Vite, Lovable, StackBlitz (Bolt), Anysphere (Cursor), Replit or Vercel (v0). Product names are trademarks of their owners and are used only to identify the tools this guide covers. OpenRouter and Railway facts are paraphrased from their own pages as checked on Oct 28, 2026, and can change. This page is general information, not professional security advice, legal advice, a security audit or a guarantee. Check your own setup against the vendor's current docs.